 Trading modes
Paper trading vs backtesting vs live trading
Three modes answer different questions. Learn what each one tests and how to record discrepancies.
Keep account custody and permission to trade separate when reviewing a bot connection.
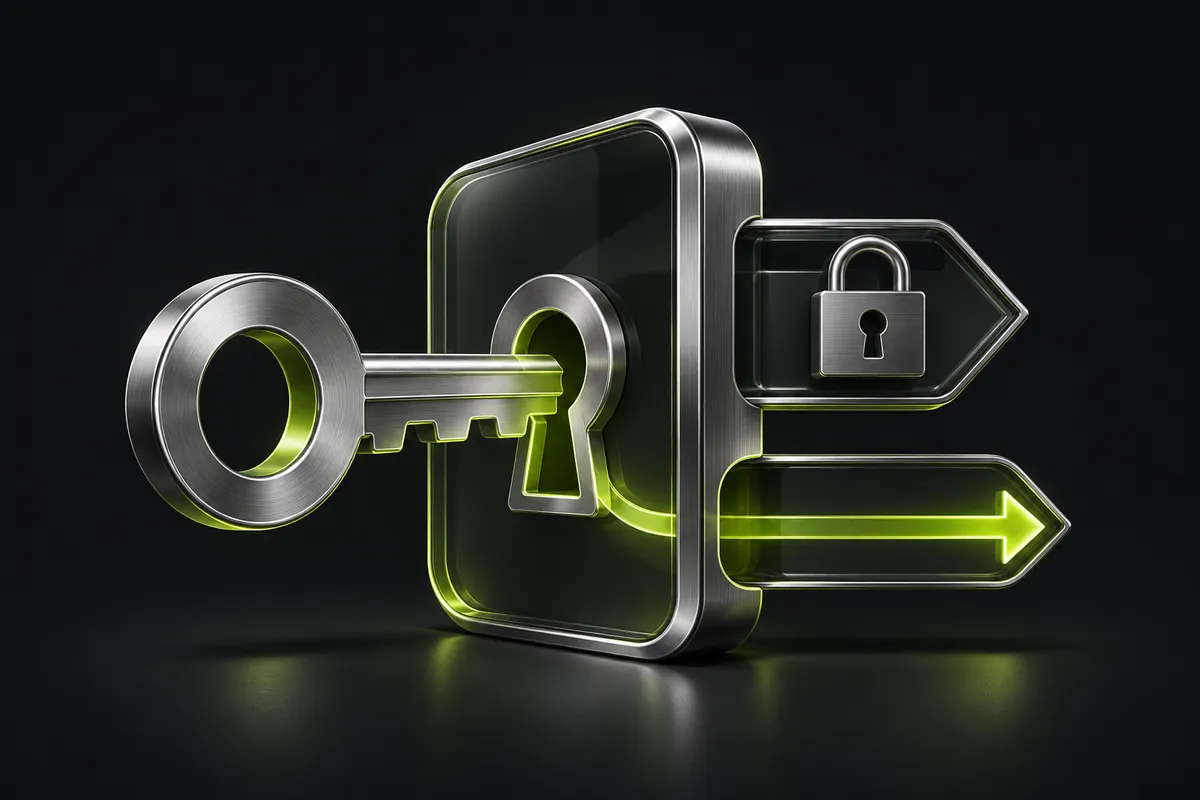
Give a trading bot only the API permissions required for the task. Start with read access when reviewing account data, leave withdrawals disabled, and grant trading access only after checking the exact integration and its controls. Keep the secret out of prompts, screenshots, chat messages and repositories.
Disabling withdrawals removes one route for moving funds. It does not make trading access harmless: a key that can place orders can change positions, incur fees and cause losses. Evaluate custody and permission to act as separate questions before connecting any automation service.
Write down the job first. Portfolio analysis may require balances and historical trades without permission to place an order. An execution workflow may also require creating, querying and canceling orders. Deposits, withdrawals, transfers, margin and derivatives permissions are separate capabilities to examine where the venue offers them.
Permission names vary. Kraken, for example, distinguishes querying funds, modifying orders, canceling orders and withdrawing funds. Do not copy another exchange's checkbox sequence blindly. Compare the vendor's request with your venue's current documentation and ask why each permission is needed.
Use a separate key for each service and purpose. A descriptive name such as “analytics-read-2026-11” helps you identify access later without exposing the secret. A shared key makes it harder to identify which connection caused an action or to revoke one service selectively.
Imagine a fictional account with 2,000 USDT. A trade-enabled key buys 20 units at 100, then sells them at 95. The price loss is 20 × 5 = 100 USDT, or 5% of the starting balance, before fees. No withdrawal occurred.
This is not a forecast or an incident claim. It is a simple demonstration of what trading permission authorizes. Larger exposure, repeated trades or leverage can create other outcomes. A no-withdrawal key does not by itself enforce your strategy's risk budget.
Ask where position limits and approved instruments are enforced. A setting inside a bot may not constrain someone using a stolen key outside that bot. Where supported, account-level segregation and venue-level restrictions can add boundaries; confirm their exact scope instead of assuming every exchange provides them.
Open the exchange and the service through verified destinations. Check the domain before creating or entering credentials. Enable strong account authentication, but remember that an authorized API request may not require the same interactive confirmation as a browser login.
Where the integration supports it, restrict the key to the documented outbound IP addresses. Ask how address changes are communicated before relying on that restriction. If a provider cannot supply a compatible setup, treat that as an unresolved requirement; do not silently remove protection to get a successful connection.
Store secrets in the intended secure connection mechanism or a suitable secret manager. Avoid plaintext notes and source files. Review logs and error reports for accidental exposure. Never paste a key into an AI prompt to ask whether it looks correct; use fake placeholders when discussing configuration.
Record the key's purpose, creation date, permitted actions and revocation location without storing its secret in the checklist. Begin with a read-only connection when the task allows it. An analysis request should not require a test withdrawal or an unnecessary live trade.
Check how you can stop new actions if the service is unavailable. Deleting a saved connection in the service and revoking the key at the exchange are not necessarily the same action. Know the exchange-side procedure and preserve independent access to the account.
If a secret is exposed, revoke the affected key promptly at the venue and inspect orders, fills, positions and balances through a trusted session. Review pending orders separately: removing future API access does not necessarily cancel actions already accepted. Generate a replacement only after investigating the exposure route and updating the required controls.
Clerix describes a model in which funds remain at the exchange and a trading scenario needs API trading rights without withdrawal rights. Its testing engines and live execution are in development; a venue logo does not establish a ready connection. Review Clerix features and current availability before creating any key. For early preparation, the strategy specification guide needs no account secret.
No. Keeping funds on an exchange does not remove the consequences of authorized trading actions. Review what the key can do and which restrictions apply outside the bot.
Follow the venue's policy and your access-review process. Revoke unused or exposed keys promptly. Routine rotation must include updating dependent connections and checking that old access is actually removed.
Use redacted identifiers, error messages and the official connection flow. Do not send the API secret in an ordinary support conversation or public issue.
Trading modesThree modes answer different questions. Learn what each one tests and how to record discrepancies.
 Strategy rules
Turn a vague idea into a testable specification with questions, a sample prompt and boundary cases.
 Choosing tools
Understand what a trading bot does and compare its rules, tests, exchange access and costs before activation.